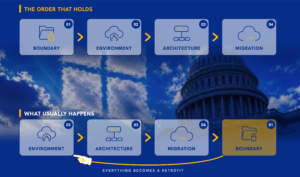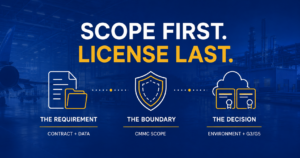

Scope is the one CMMC decision you pay for twice when it is wrong. You pay once to build the boundary, and again to move it after assessment prep, a prime’s questionnaire, or your own Affirming Official finds CUI on the wrong side of it. Every other part of a
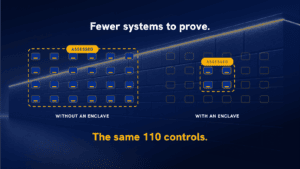
A CMMC enclave doesn’t lower your obligation. It lowers how much of your environment has to prove it. CMMC Level 2 applies to the systems that store, process, or transmit CUI, not to every system an organization runs. An enclave draws a hard boundary around those specific systems, so the
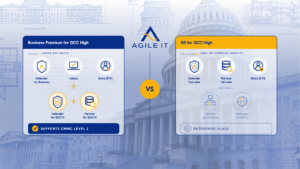
Microsoft built Business Premium for GCC High because most smaller contractors don’t need everything a G5 license includes. They need the specific controls CMMC Level 2 requires, and G5 is one way to get there, not the only one. What Business Premium for GCC High Actually Covers Microsoft announced Business
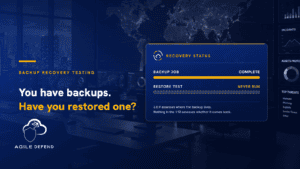

CMMC doesn’t ask whether your backups restore. Most organizations read that as good news. It isn’t relief. It’s a gap in the checklist, not a gap in the risk. What CMMC Actually Checks, and What It Doesn’t NIST SP 800-171 requires protecting the confidentiality of backup CUI at storage locations,
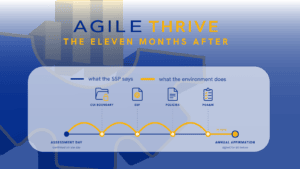
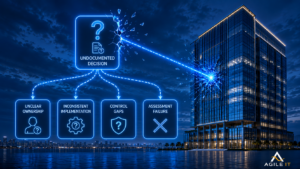
A CMMC assessment confirms an environment on one day. The attestation that follows requires it to still be true eleven months later, backed by the weight of the False Claims Act. Documentation says one thing. The environment does another, not because anyone lied, but because systems change faster than the
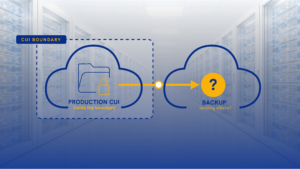
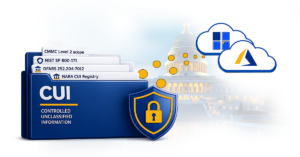
Every organization we migrate into GCC High already has backups running before we touch the tenant. Almost none of them have confirmed where those backups land. That gap isn’t hypothetical. DFARS 252.204-7012 requires covered contractor information systems to implement NIST SP 800-171. Control 3.8.9 states it plainly: protect the confidentiality
Scope is the one CMMC decision you pay for twice when it is wrong. You pay once to build the boundary, and again to move it after assessment prep, a prime’s questionnaire, or your own Affirming Official finds CUI on the wrong side of it. Every other part of a
A CMMC enclave doesn’t lower your obligation. It lowers how much of your environment has to prove it. CMMC Level 2 applies to the systems that store, process, or transmit CUI, not to every system an organization runs. An enclave draws a hard boundary around those specific systems, so the
Microsoft built Business Premium for GCC High because most smaller contractors don’t need everything a G5 license includes. They need the specific controls CMMC Level 2 requires, and G5 is one way to get there, not the only one. What Business Premium for GCC High Actually Covers Microsoft announced Business
CMMC doesn’t ask whether your backups restore. Most organizations read that as good news. It isn’t relief. It’s a gap in the checklist, not a gap in the risk. What CMMC Actually Checks, and What It Doesn’t NIST SP 800-171 requires protecting the confidentiality of backup CUI at storage locations,
A CMMC assessment confirms an environment on one day. The attestation that follows requires it to still be true eleven months later, backed by the weight of the False Claims Act. Documentation says one thing. The environment does another, not because anyone lied, but because systems change faster than the
Every organization we migrate into GCC High already has backups running before we touch the tenant. Almost none of them have confirmed where those backups land. That gap isn’t hypothetical. DFARS 252.204-7012 requires covered contractor information systems to implement NIST SP 800-171. Control 3.8.9 states it plainly: protect the confidentiality