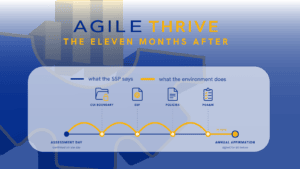
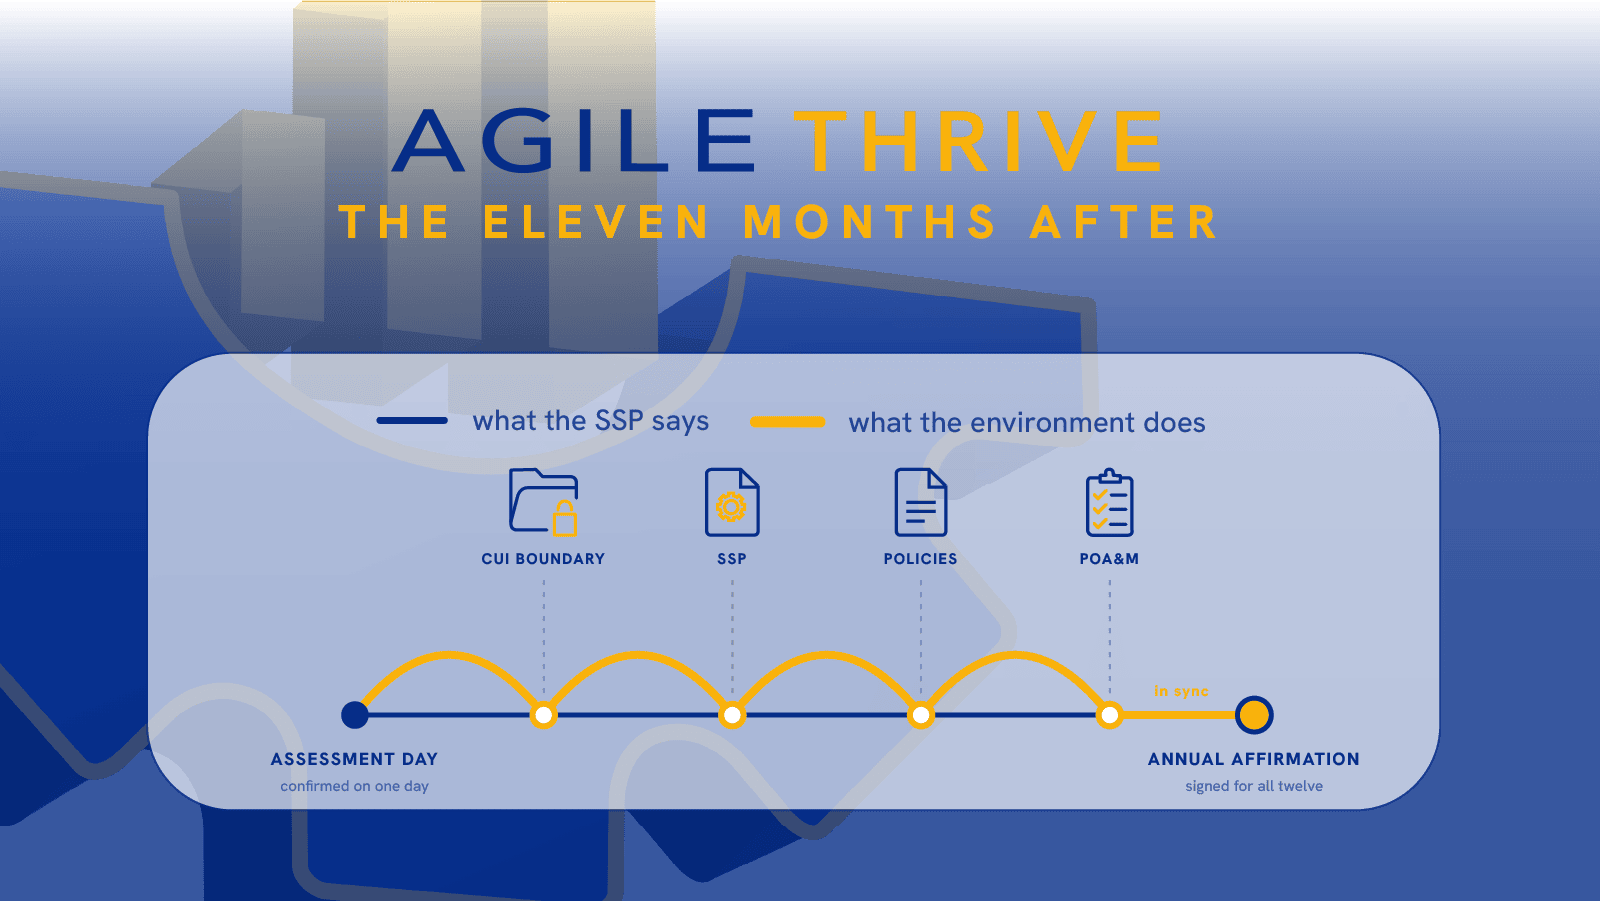
A CMMC assessment confirms an environment on one day. The attestation that follows requires it to still be true eleven months later, backed by the weight of the False Claims Act.
Documentation says one thing. The environment does another, not because anyone lied, but because systems change faster than the paperwork describing them. AgileThrive closes that distance on a set schedule, so the explanation is already documented before anyone asks for it.
What AgileThrive Actually Covers
AgileThrive is the Thrive piece of Agile IT’s three-part service family: Secure for deployment and licensing, Defend for managed cloud operations, Thrive for staying audit-ready once the environment is live and a contract depends on it.
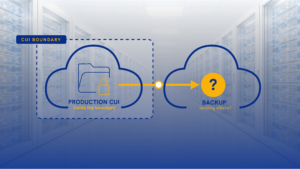
The work itself is specific, not a general retainer. It keeps the CUI boundary defined as systems and users change, and keeps the System Security Plan current with whatever that boundary actually looks like this quarter. Living policies and procedures get reviewed on set cadences, not drafted once and filed away. POA&M items and corrective actions move toward closure instead of accumulating. The periodic reviews CMMC Level 2 already requires happen on a documented schedule, rather than whenever someone remembers to run one.
Not a Gap Assessment, and Not the Assessment Itself
A gap assessment captures a single moment. AgileThrive is the ongoing structure that keeps scope, evidence, and documentation aligned with the environment between assessments, not a replacement for either.
It doesn’t replace the C3PAO assessment. An organization still goes through that process on its own schedule. AgileThrive is what keeps the answer to “is this still true” from turning into a scramble in the weeks before that assessment comes back around.
Who Owns What
Agile IT owns documentation structure, evidence tracking, and review cadence within the agreed scope. The organization owns governance decisions and final sign-off on its own attestation.
That division isn’t a formality. An accredited assessor validates evidence; they don’t guide it, generate it, or own it, and Agile IT is not a C3PAO. AgileThrive keeps the paperwork honest about the environment. It doesn’t decide what the environment should be, and it doesn’t stand in for the sign-off that has to come from inside the organization.
How the Engagement Actually Runs
Onboarding establishes current scope, documentation, and gaps against NIST SP 800-171 requirements. From there, open POA&M items move toward closure while documentation gets brought current, and a recurring review cycle takes over once scope, evidence, and governance actually match what the environment does. That cycle runs on a set schedule going forward, not on whoever happens to remember it’s due.
Whose Evidence Trail Would Hold Up if Someone Asked for It Tomorrow?
FAQ
What actually changes between an assessment and an attestation? An assessment captures the environment at a single point in time. An attestation claims the picture from the last assessment is still accurate. Scope shifts, staff turns over, new systems come online, and policies written once sit untouched for a year. That distance is what surfaces when the next assessment, or the next attestation, asks the environment to explain itself.
Does AgileThrive handle the periodic reviews CMMC Level 2 requires? Yes. Several CMMC Level 2 objectives require reviews that have to be performed and documented on a recurring schedule. AgileThrive runs those reviews on a set cadence, checking scope, risk, and documentation each time, with ownership explicit throughout.
How does AgileThrive relate to Agile IT’s other services? AgileThrive is the Thrive piece of a three-part service family. Secure covers deployment and licensing. Defend covers managed cloud operations. Thrive keeps the environment audit-ready once it’s live and a contract depends on it.
What happens first in an AgileThrive engagement? Onboarding. It establishes current scope, documentation, and gaps against NIST SP 800-171 requirements before anything else moves.
Pressure-Test Your Evidence Trail → https://agileit.com/agile-thrive/