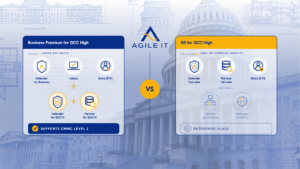
Choosing between Azure Virtual Desktop (AVD) and Windows 365 in GCC High decides what your CMMC assessor reviews. Configured correctly, either one can take the laptops your users touch out of assessment scope. Configured loosely, either one adds systems to it.
Both run in Microsoft’s government cloud. They differ in how sessions run, how they are priced, and how much your team has to manage.
Where CUI Lives Decides What Gets Assessed
The DoW CIO’s CMMC Program FAQ addresses virtual desktops directly. An endpoint running a VDI client is an Out-of-Scope Asset if it is configured to pass nothing beyond keyboard, video, and mouse data to the virtual desktop. CMMC FAQ If the endpoint can process, store, or transmit CUI, it is a CUI Asset and it is in scope.
The same FAQ spells out the configuration that keeps an endpoint out (FAQ F-A2):
- Copy and paste, file transfer, and drive mapping blocked at the server
- No saving, printing, or screenshots of CUI to the local device
- Multifactor authentication to the virtual desktop that is separate from the unmanaged endpoint, such as a hardware token or PKI token with a PIN
- Access limited to authorized users and allowable locations
Nobody picks a virtual desktop for its printer settings. In GCC High, the printer settings are half the decision.
Scope stays open after certification. Level 2 assessments recur every three years, with an affirmation of continued compliance every year. A change that brings in systems or security tools that were never assessed can require a new assessment.
The desktop platform you choose now shows up in every one of those reviews.
How AVD and Windows 365 Differ
| Azure Virtual Desktop | Windows 365 | |
| What it is | Desktop and app virtualization built on Azure | A persistent cloud PC: one dedicated Windows VM per user |
| Session model | Multi-session Windows 10 Enterprise and Windows 11, available only in AVD | One user per cloud PC |
| Pricing | KEVIN TO CONFIRM: confirm AVD billing model | Fixed per user |
| Management | Azure portal, PowerShell, and REST APIs manage host pools and apps; capacity scales by time of day or organizational change | Provisioned automatically and managed through Intune |
| Existing apps | Brings Windows Server apps and Remote Desktop Services to any computer | Includes Microsoft 365 productivity apps |
| Skills needed | VDI administration | No VDI skills needed to onboard |
AVD gives your team full configuration control and the most to manage. Windows 365 trades some of that control for a desktop that is provisioned per user and priced the same every month.
Where Each One Fits
AVD fits environments that need high-volume, multi-session concurrency. That includes call and contact centers, task-based roles, and organizations where users do not have the same hardware or software.
Windows 365 fits narrower access. It suits subcontractors who need CUI access without a full VDI build, third-party consultants connecting through a license and a protected entry point, and employees from an acquired or merged organization who need to connect their own devices within a few hours.
The last two cases put personal devices in front of CUI. Those devices stay out of scope only when the controls listed above are configured and verified.
The desktop you pick changes what your assessor reviews.
We build AVD and Windows 365 in GCC High and configure the session controls the DoW FAQ describes. Microsoft AOS-G partner. Cyber AB Registered Practitioner Organization.
Pressure-test your CUI boundary
Identity and Device Controls Carry the Boundary
Both platforms depend on the same Microsoft security stack, and the boundary is only as strong as its configuration.
Microsoft Entra ID Conditional Access applies access rules to specific users and devices, which is where location limits and MFA requirements live. Microsoft Intune manages the cloud PCs and the endpoints that connect to them. With Windows 365, workstations and data stay in Microsoft’s cloud rather than on the user’s device.
Microsoft Defender for Endpoint covers prevention, monitoring, and response. AVD host pools are managed in Azure, so the same identity and device policies need to reach them.
FedRAMP Moderate Is the Floor for the Cloud Behind the Desktop
DFARS 252.204-7012 requires that any cloud service provider storing, processing, or transmitting CUI meet security requirements equivalent to the FedRAMP Moderate baseline (DFARS 252.204-7012; FAQ E-A1). That applies to the virtual desktop service the same way it applies to email and file storage.
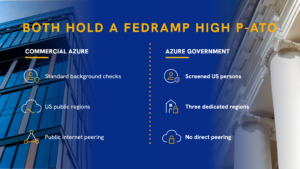
Both clear that floor. Windows 365 Government for GCC High runs on Azure Government with FedRAMP High authorization at DoW Impact Level 4 (Microsoft: What is Windows 365 Government?). Azure Virtual Desktop is in scope for the Azure Government FedRAMP High authorization (Microsoft: Azure Government services by audit scope).
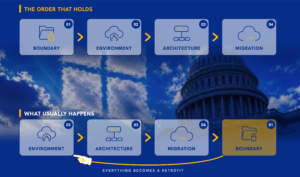
What to Settle Before You Deploy
- Where your CUI boundary sits today, and which users need to reach it
- Whether your team can run host pools and scaling, or needs desktops managed per user
- Whether your SSP, policies, and monitoring describe the virtual desktop the way the assessor will find it configured
For the wider picture, see the GCC High guide and how Microsoft’s government cloud security stack fits together. AgileThrive covers CMMC readiness, and AgileDefend covers ongoing managed security.
Frequently Asked Questions
Is Windows 365 available in GCC High?
Yes. Windows 365 runs as a cloud PC service in GCC High, priced per user.
Does AVD reduce CMMC scope?
It can. The DoW CIO’s FAQ treats an endpoint as out of scope when the virtual desktop passes only keyboard, video, and mouse data and blocks copy, print, and file transfer at the server (FAQ F-A2 ). The same rule applies to Windows 365.
Can a personal device access CUI through a virtual desktop?
Yes, if the session controls in the FAQ are in place and MFA to the virtual desktop is separate from the device. If the device can save, print, or capture CUI, it becomes a CUI Asset and is in scope.
Your endpoints are either in scope or out of it, and the configuration decides which. Has anyone confirmed which side yours are on?