CMMC, GCC High, and Azure Government
Case Studies
From Real Defense Contractors

Every case study in this library covers a real compliance challenge, a real environment, and a real outcome. Defense contractors passing audits, protecting CUI, and keeping contract eligibility through CMMC compliance, GCC High licensing, Azure Government migrations, and Microsoft 365. 

CMMC Now

Browse by Topic.

CMMC Compliance 

Everything defense contractors need to know about CMMC Level 1 and Level 2 certification. Self-attestation requirements, C3PAO assessments, NIST 800-171 controls, and what the November 2026 deadline means for your contracts.

GCC High 

Guides and analysis on Microsoft 365 GCC High licensing, configuration, and compliance. Who needs it, how to get it, and what to build inside it.

Azure Government 

Coverage of Azure Government architecture, migrations, and compliance requirements for defense contractors. Environment design, identity configuration, and what separates authorized from compliant.

FedRAMP 

Practical guidance on FedRAMP authorization pathways, readiness requirements, and continuous monitoring obligations for cloud service providers serving federal agencies.

Microsoft 365 Defense

How Microsoft 365 operate inside regulated environments. Teams, SharePoint, OneDrive, and Purview in GCC High and GCC configurations for DIB contractors.

Licensing 

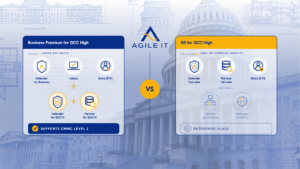
Microsoft licensing strategy for defense contractors. GCC High vs. GCC, license tier decisions, AOS-G partner requirements, and how to avoid overspending on seats you don’t need.

Migrations 

Step-by-step guidance on moving from commercial Microsoft environments into GCC High, Azure Government, and other regulated platforms without disrupting business continuity. 

Identity & Access Management

Identity configuration, access controls, and Entra ID deployments in regulated environments.

Featured

Practical guidance on CMMC, GCC High, FedRAMP, and Azure Government for defense contractors.

All Posts

About These Engagements.

Agile IT works with defense contractors, aerospace organizations, legal firms, and government entities working through CMMC compliance,
GCC High licensing, Azure Government migrations, FedRAMP authorization, and Microsoft 365 for regulated environments. The case studies
in this library cover real defense contractor cybersecurity engagements across CMMC Level 1 self-attestation, CMMC Level 2 certification,
DFARS 7012 compliance obligations, and federal cloud migrations. Each engagement reflects real compliance decisions, real environments,
and real outcomes. If you’re evaluating a compliance partner, the proof is here.

Our Insight

Blog
Maggie McGrath

Scoping CUI Correctly the First Time 

Scope is the one CMMC decision you pay for twice when it is wrong. You pay once to build the boundary, and again to move it after assessment prep, a prime’s questionnaire, or your own Affirming Official finds CUI on the wrong side of it.  Every other part of a

Read More »
Blog
Maggie McGrath

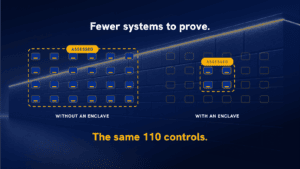
CMMC Enclave: What It Actually Reduces, and What It Doesn’t 

A CMMC enclave doesn’t lower your obligation. It lowers how much of your environment has to prove it.  CMMC Level 2 applies to the systems that store, process, or transmit CUI, not to every system an organization runs. An enclave draws a hard boundary around those specific systems, so the

Read More »
Blog
Desiree Grimaldi

You Have Backups. When Was the Last Time You Tested the Recovery? 

CMMC doesn’t ask whether your backups restore. Most organizations read that as good news.  It isn’t relief. It’s a gap in the checklist, not a gap in the risk.  What CMMC Actually Checks, and What It Doesn’t  NIST SP 800-171 requires protecting the confidentiality of backup CUI at storage locations,

Read More »
Blog
Maggie McGrath

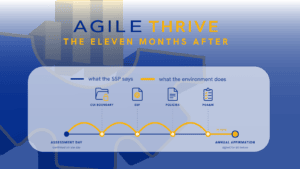
The Eleven Months After Your CMMC Assessment

A CMMC assessment confirms an environment on one day. The attestation that follows requires it to still be true eleven months later, backed by the weight of the False Claims Act.  Documentation says one thing. The environment does another, not because anyone lied, but because systems change faster than the

Read More »
Blog
Maggie McGrath

The Backup Nobody Checked Against the Boundary 

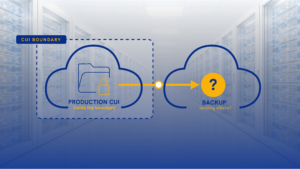
Every organization we migrate into GCC High already has backups running before we touch the tenant. Almost none of them have confirmed where those backups land.  That gap isn’t hypothetical. DFARS 252.204-7012 requires covered contractor information systems to implement NIST SP 800-171. Control 3.8.9 states it plainly: protect the confidentiality

Read More »

Most Recent News

Blog
Maggie McGrath

Scoping CUI Correctly the First Time 

Scope is the one CMMC decision you pay for twice when it is wrong. You pay once to build the boundary, and again to move it after assessment prep, a prime’s questionnaire, or your own Affirming Official finds CUI on the wrong side of it.  Every other part of a

Read More »
Blog
Maggie McGrath

CMMC Enclave: What It Actually Reduces, and What It Doesn’t 

A CMMC enclave doesn’t lower your obligation. It lowers how much of your environment has to prove it.  CMMC Level 2 applies to the systems that store, process, or transmit CUI, not to every system an organization runs. An enclave draws a hard boundary around those specific systems, so the

Read More »
Blog
Desiree Grimaldi

You Have Backups. When Was the Last Time You Tested the Recovery? 

CMMC doesn’t ask whether your backups restore. Most organizations read that as good news.  It isn’t relief. It’s a gap in the checklist, not a gap in the risk.  What CMMC Actually Checks, and What It Doesn’t  NIST SP 800-171 requires protecting the confidentiality of backup CUI at storage locations,

Read More »
Blog
Maggie McGrath

The Eleven Months After Your CMMC Assessment

A CMMC assessment confirms an environment on one day. The attestation that follows requires it to still be true eleven months later, backed by the weight of the False Claims Act.  Documentation says one thing. The environment does another, not because anyone lied, but because systems change faster than the

Read More »
Blog
Maggie McGrath

The Backup Nobody Checked Against the Boundary 

Every organization we migrate into GCC High already has backups running before we touch the tenant. Almost none of them have confirmed where those backups land.  That gap isn’t hypothetical. DFARS 252.204-7012 requires covered contractor information systems to implement NIST SP 800-171. Control 3.8.9 states it plainly: protect the confidentiality

Read More »

Your Environment Could Be the Next Case

Every engagement above started the same way, a contractor facing an audit, a deadline, or a contract requirement they couldn’t risk missing. If that’s where you are, start with an assessment of your Microsoft environment.