Client Results
Their Words, Not Ours.

Each of these engagements involved a Microsoft GCC or GCC High migration, configured with CMMC alignment in mind from the start. The environments are different. The outcome each client describes is the same: a migration that held up once compliance work actually began.

In Their Own Words

Liberty Alliance

Working with Agile IT was a great experience from start to finish. Your team’s expertise in Microsoft GCC High, Intune, and configuration helped ensure our environment was configured correctly and aligned with our compliance objectives. 

The guidance and support you provided throughout the deployment gave us confidence that our Microsoft 365 GCC High environment is positioned to support our journey toward achieving CMMC Level 2 certification. Your responsiveness, technical knowledge, and willingness to work through challenges made this a smooth implementation.  

We appreciate the partnership and look forward to working with Agile IT on future projects. 

Airtech Supply

Agile IT didn’t just migrate us to Microsoft GCC High—they delivered a CMMC-aligned environment with industry best practices already in place, saving us countless hours of configuration and helping us establish a secure foundation.

Affordable Engineering Services

Professional, Responsive, Attentive and just a pleasure to work with.  The migration services were explained and executed with attention focused on us the end user. AgileIT took a very complex and stressful situation and made us feel at ease at each level of the project.  

Very knowledgeable and provided many resources to assist with migration. Would recommend to any company wanting to migrate to GCC or GCC High.  

Featured

Practical guidance on CMMC, GCC High, FedRAMP, and Azure Government for defense contractors.

More of Our Work

About These Engagements.

Agile IT works with defense contractors, aerospace organizations, legal firms, and government entities working through CMMC compliance,
GCC High licensing, Azure Government migrations, FedRAMP authorization, and Microsoft 365 for regulated environments. The case studies
in this library cover real defense contractor cybersecurity engagements across CMMC Level 1 self-attestation, CMMC Level 2 certification,
DFARS 7012 compliance obligations, and federal cloud migrations. Each engagement reflects real compliance decisions, real environments,
and real outcomes. If you’re evaluating a compliance partner, the proof is here.

Our Insight

Blog
Raven Riley

GCC High Licensing and G3 vs. G5 Start With CMMC Scope 

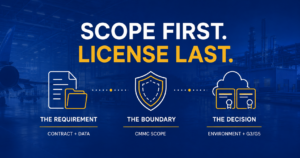
GCC High Licensing and G3 vs. G5 Start With CMMC Scope  Microsoft licensing is the last decision in the chain, and it is the one most organizations make first. The contract, the data, and the Cybersecurity Maturity Model Certification (CMMC) Assessment Scope decide the Microsoft cloud and the licensing tier inside

Read More »
Blog
Raven Riley

What Counts as CUI in Microsoft 365 and Azure Government

Most CUI scope decisions get made in one meeting, by whoever is in the room, and documented afterward to match. That boundary holds until a C3PAO asks who justified it. The designating agency decides what qualifies. Data flow decides what’s in scope. The Microsoft environment follows both, not the reverse.

Read More »
CMMC assessment failures
Blog
Raven Riley

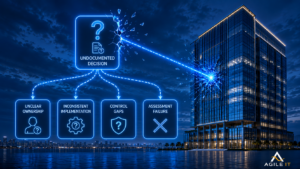
Where CMMC Assessments Break Down in Microsoft Environments

Assessment failures rarely start with missing controls. They start with decisions no one wrote down. CMMC Level 2 assessments that stall inside a Microsoft environment tend to start from the same baseline, not a shortage of controls. Conditional access is enforced, audit logging is active, and identity governance is running

Read More »
CMMC Level 1 vs Level 2
Blog
Maggie McGrath

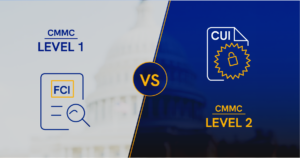
CMMC Level 1 vs Level 2: What Defense Contractors Need to Know 

CMMC Level 1 and Level 2 don’t follow the same logic, and treating them as steps on the same ladder is where scoping goes wrong. This guide breaks down what triggers each level, how the assessments differ, and the decisions defense contractors need to make before either one gets scheduled.

Read More »

Most Recent News

Blog
Raven Riley

GCC High Licensing and G3 vs. G5 Start With CMMC Scope 

GCC High Licensing and G3 vs. G5 Start With CMMC Scope  Microsoft licensing is the last decision in the chain, and it is the one most organizations make first. The contract, the data, and the Cybersecurity Maturity Model Certification (CMMC) Assessment Scope decide the Microsoft cloud and the licensing tier inside

Read More »
Blog
Raven Riley

What Counts as CUI in Microsoft 365 and Azure Government

Most CUI scope decisions get made in one meeting, by whoever is in the room, and documented afterward to match. That boundary holds until a C3PAO asks who justified it. The designating agency decides what qualifies. Data flow decides what’s in scope. The Microsoft environment follows both, not the reverse.

Read More »
CMMC assessment failures
Blog
Raven Riley

Where CMMC Assessments Break Down in Microsoft Environments

Assessment failures rarely start with missing controls. They start with decisions no one wrote down. CMMC Level 2 assessments that stall inside a Microsoft environment tend to start from the same baseline, not a shortage of controls. Conditional access is enforced, audit logging is active, and identity governance is running

Read More »
CMMC Level 1 vs Level 2
Blog
Maggie McGrath

CMMC Level 1 vs Level 2: What Defense Contractors Need to Know 

CMMC Level 1 and Level 2 don’t follow the same logic, and treating them as steps on the same ladder is where scoping goes wrong. This guide breaks down what triggers each level, how the assessments differ, and the decisions defense contractors need to make before either one gets scheduled.

Read More »

See What Your Own Environment Looks Like Next

Every engagement above started the same way, a contractor facing an audit, a deadline, or a contract requirement they couldn’t risk missing. If that’s where you are, start with an assessment of your Microsoft environment.